Can I try it before buying?
Yes — seven days with the full product. Every feature, no row limits, no watermark on the output. It is the same build you would buy, with a licence that expires. No purchase, no email address, no account: install it, copy the device ID it shows you, and paste it into the page.
We dropped the idea of a permanently free edition with file and row limits. A limited version answers the wrong question — it tells you whether ShiftMask runs, not whether it survives your actual data. Seven days on your own files answers the question you have.
Is it safe to put company data into ChatGPT?
Not the real data. Anything you paste leaves your control, and most public AI tools give you no contractual guarantee about where it goes. ShiftMask exists so you never have to — you send a structurally identical copy in which no value is a real name, account or identifier, and you get working code back all the same.
We use Microsoft Copilot. Is our data not already protected?
Two different things get called Copilot, and they need different answers.
If it means pasting a real spreadsheet into Copilot and asking it to anonymise the contents — by the time it can do that, the data has already left your machine. The masking happens after the exposure instead of preventing it. ShiftMask runs before anything is sent, and that is the whole difference.
If it means Microsoft 365 Copilot with enterprise data protection, the guarantee is real and worth having: your prompts stay inside your tenant and are not used to train foundation models. But it answers a different question from the one a client contract asks. An NDA is usually about where a client’s data may be processed and who may see it, not about whether a model trains on it. If you hold data for several clients, or for one whose contract names the systems their data may enter, “it stayed in our tenant” is an argument you have to make and win. With a masked copy there is no argument to make, because what you pasted was not their data.
For the practical side of Copilot inside Excel, see How to use Copilot in Excel safely with sensitive data.
Can't I just ask Copilot or ChatGPT to anonymise the file?
You can ask, and people do. What comes back is a best effort, not a guarantee. A language model works through a workbook the way it reads text: it can stop part-way, skip rows, or treat the same customer differently in two places — and it says it is done when it believes it is.
One analyst told us exactly that. He asked Copilot to anonymise the personal data in a workbook, then asked whether it had done everything. It checked, found it had not, and did more. It took more than four rounds, and he still had no way to know whether the last round was the last.
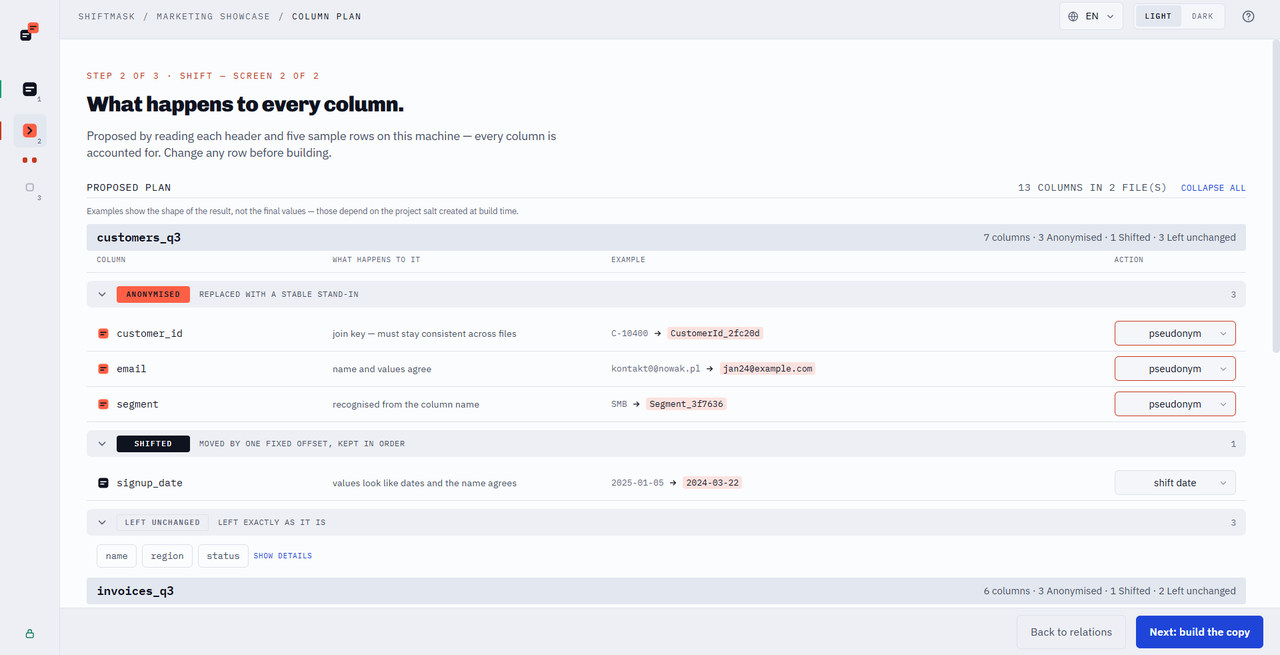
ShiftMask works the other way round. Before anything runs, you see every column and what will happen to it. Every value in every column you chose is then processed in every row, the same way every time, and the report at the end says what was done — including any cell that could not be converted. The question you are left with is not “did it finish?” but “did I pick the right columns?”, and that one you can check with your own eyes.
And there is the earlier point: to have a model anonymise a file, you first have to give it the file.
My company does not let me install software. Can I still use it?
Possibly, and the honest answer has three parts.
The installer needs no administrator rights. It installs for your user only and writes nothing to Program Files. That settles the technical question, but not the policy one.
If the policy is about installers specifically, take the portable build instead: unpack the ZIP, run the file inside. No installer, no registry entry, nothing written outside the folder you unpacked it into.
If the policy is about running any unapproved program — and in the kind of organisation that needs this tool most, it usually is — then someone has to approve it, and the way through is to ask rather than to go around. We wrote the page for that person: what your IT department will ask. It covers what gets installed and where, exactly what leaves the machine and what does not, how to verify the code signature yourself, and which third-party components ship inside.
Does my data leave my computer?
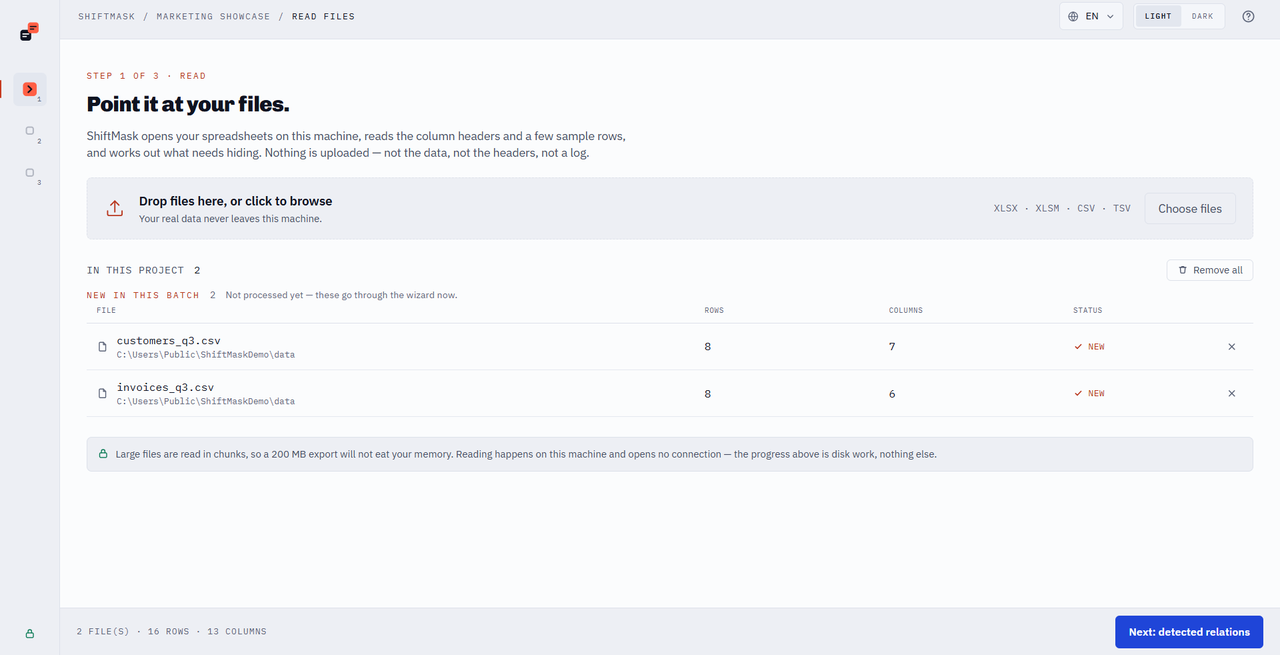
No. ShiftMask is a desktop application. It reads your files locally, builds the masked copy in a local DuckDB database, and writes the output to your disk. You decide what, if anything, gets sent anywhere.
Does masking break my Power BI time intelligence?
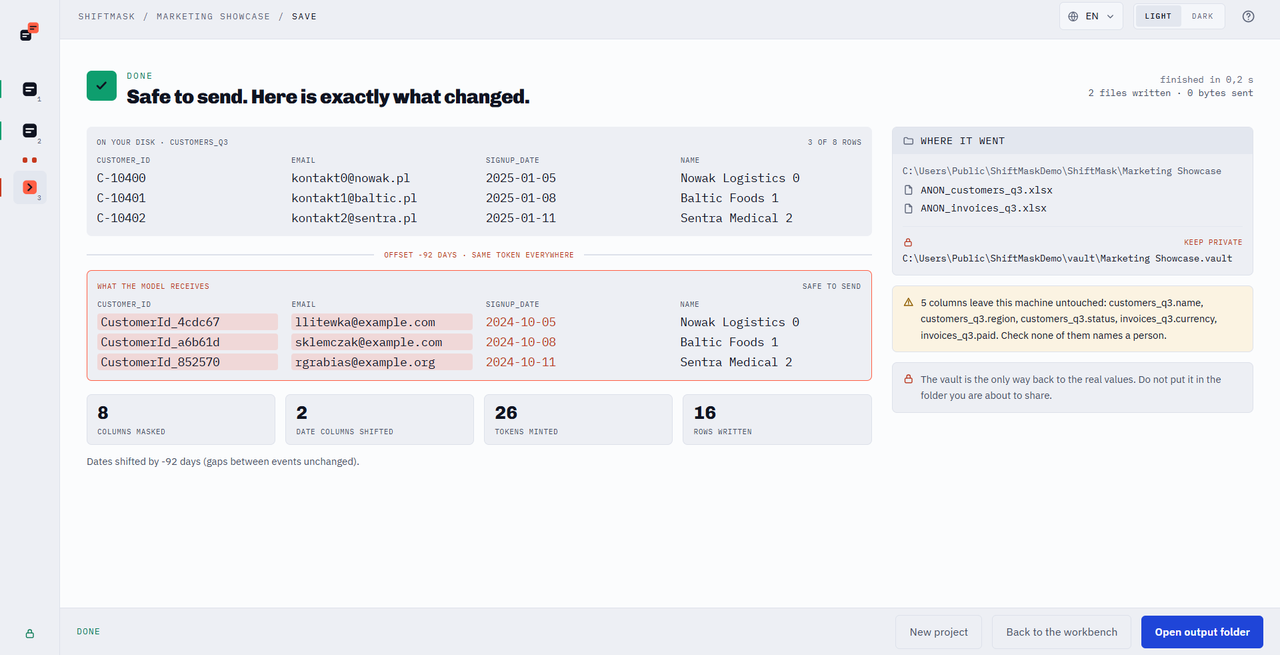
That is the specific failure ShiftMask was built to avoid. Random date replacement destroys intervals, which breaks YTD, YoY and every rolling calculation. ShiftMask moves every date by one shared offset instead, so the distance between any two events is unchanged and time-based measures return the same shape.
How do I anonymize an Excel file for AI?
Open the workbook in ShiftMask, confirm which columns hold personal data — it proposes a classification automatically — and export. You get a new workbook with the same sheets, columns and relationships, and with names, identifiers and dates replaced by consistent stand-ins. The map back to the real values stays in an encrypted vault on your machine — that is what lets you swap the real data back in later, and it is why the export is pseudonymised rather than irreversibly anonymised.
Does this make me GDPR compliant?
No tool can make that promise for you, and be careful with any that does. What ShiftMask does is replace the personal data in the copy you share with stand-ins, which is usually the hard part of using public AI tools lawfully. Because the map back is kept — encrypted, on your machine — that copy is pseudonymised under GDPR rather than anonymised, so it remains personal data. Your obligations under GDPR, and under HIPAA if you work with health data, still depend on your own processes.
Can I get a refund?
Yes — within 14 days, no questions asked. Write to shiftmask@4optima.pl and we will arrange it. Your purchase is handled by Lemon Squeezy as merchant of record, so the money comes back through them.
One thing worth saying plainly: a licence token, once issued, cannot be revoked. It is verified entirely offline, which is exactly what lets ShiftMask run on machines with no internet — and the price of that is no kill switch. After a refund we are relying on you to stop using it. We would rather ask than break offline activation to prevent it.
I am replacing my computer. What happens to my licence?
You get a new token, at no charge, and there is no limit on how many times. Hardware fails and laptops get stolen; a limit would punish the people that happens to without stopping anyone acting in bad faith.
ShiftMask prepares the whole request for you — there is a transfer button on the activation screen, which is where you will be if the old machine is already gone. Send it from the address you bought with, since that is what links the request to your order, and you get a new token within one working day. A person handles this rather than an automatic system: self-service would mean keeping a record of every activation on our server, which is precisely what this product promises not to do.
How is this different from an enterprise masking platform?
Those are built for test environments, priced for enterprise budgets, and usually run as a service. ShiftMask is a desktop app for one person with one project and a deadline, sold for one payment, and it never sends your data to a server.